Axios Codebook
January 31, 2025

😎 TGIF, everyone. Welcome back to Codebook.
- 🏀 To set the record straight before tomorrow's game: Go Heels, Go America!
- 📬 Have thoughts, feedback or scoops to share? [email protected].
Today's newsletter is 1,262 words, a 5-minute read.
1 big thing: Researchers poke holes in DeepSeek's security
A flurry of security research reports this week suggest DeepSeek's open-source AI models may be susceptible to cyberattacks.
Why it matters: Cybersecurity and national security experts are already on high alert over potential security problems with the China-based AI startup — including potential model leaks and cyberattacks.
Driving the news: Security researchers at cloud security startup Wiz identified an exposed DeepSeek database that left chat histories, secret keys, backend details and other sensitive information exposed online, according to a report released Wednesday.
- Palo Alto Networks' threat researchers also released a report yesterday finding that it was fairly easy to get DeepSeek to break its own guardrails and provide tips for writing code to help hackers exfiltrate data, send phishing emails, and optimize social engineering attacks.
- Researchers at security firm Enkrypt AI published a report this morning finding that DeepSeek's new R1 reasoning model is four times more likely to write malware and other insecure code than OpenAI's o1.
The big picture: U.S. interest in DeepSeek skyrocketed in the last week after the AI startup released its R1 model, which rivals OpenAI's capabilities at a fraction of the investment cost.
- The overnight obsession sparked a fresh new round of scrutiny into DeepSeek's data privacy and content moderation policies.
Zoom in: Wiz's security researchers found the exposed database of chat logs and other sensitive information within minutes of beginning their investigation, per their report.
- The database had more than 1 million lines of activity log streams that included the exposed chat histories and other sensitive information.
- The database also gave anyone who came across it full database control and potential privilege-escalation capabilities without needing to authenticate their identity and whether they were allowed to see this database.
- DeepSeek fixed the exposure before Wiz released its findings.
Meanwhile, researchers at Palo Alto Networks' Unit 42 research unit used basic jailbreaking techniques to get DeepSeek's R1 model to help them craft phishing emails, write malware, and even provide comprehensive instructions for constructing a Molotov cocktail.
- Enkrypt AI's researchers found that DeepSeek was "highly susceptible" to prompt injections, where hackers socially engineer malicious prompts to look like legitimate requests.
- Researchers could also get DeepSeek to produce harmful content in 45% of their tests. In one test, DeepSeek wrote a blog that detailed ways that terrorist organizations could recruit new members, Enkrypt AI found.
- DeepSeek did not respond to a request for comment.
Reality check: Even U.S. models are susceptible to jailbreaking, but researchers note that it's gotten harder for them to use these techniques to trick ChatGPT, Anthropic's Claude and others.
Between the lines: The findings each highlight the faults AI models can have if companies don't conduct proper security and safety checks before release.
- "While DeepSeek R1 may be viable for narrowly scoped applications, robust safeguards — including guardrails and continuous monitoring — are essential to prevent harmful misuse," Enkrypt AI CEO Sahil Agarwal said in a statement. "AI safety must evolve alongside innovation, not as an afterthought."
What we're watching: It remains to be seen how long the U.S. obsession with DeepSeek will last — and whether there will be a major U.S. policy backlash against companies and employees using the China-based startup's app.
2. FBI takes down two major cybercrime forums
Law enforcement agencies arrested two people and seized the web infrastructure tied to two of the world's biggest cybercrime forums where hackers sold stolen passwords and hacking tools, the Justice Department said in a press release yesterday.
Why it matters: Dismantling these online hubs deals a serious blow to malicious hackers who rely on forums to turn a profit from their crimes.
Zoom in: International law enforcement, led by German authorities, carried out an operation to shut down the infamous Cracked and Nulled hacker forums this week, Europol said in a press release.
- Two people were arrested in connection with the forums, and law enforcement seized 17 servers and more than 50 electronic devices while searching seven properties over the last two days, the release said.
- Law enforcement also seized around 300,000 euros ($311,553) in cash and cryptocurrencies, as well as 12 domains tied to Cracked and Nulled.
Catch up quick: Several security researchers spotted that law enforcement placed seizure notices on the forums' homepages Wednesday.
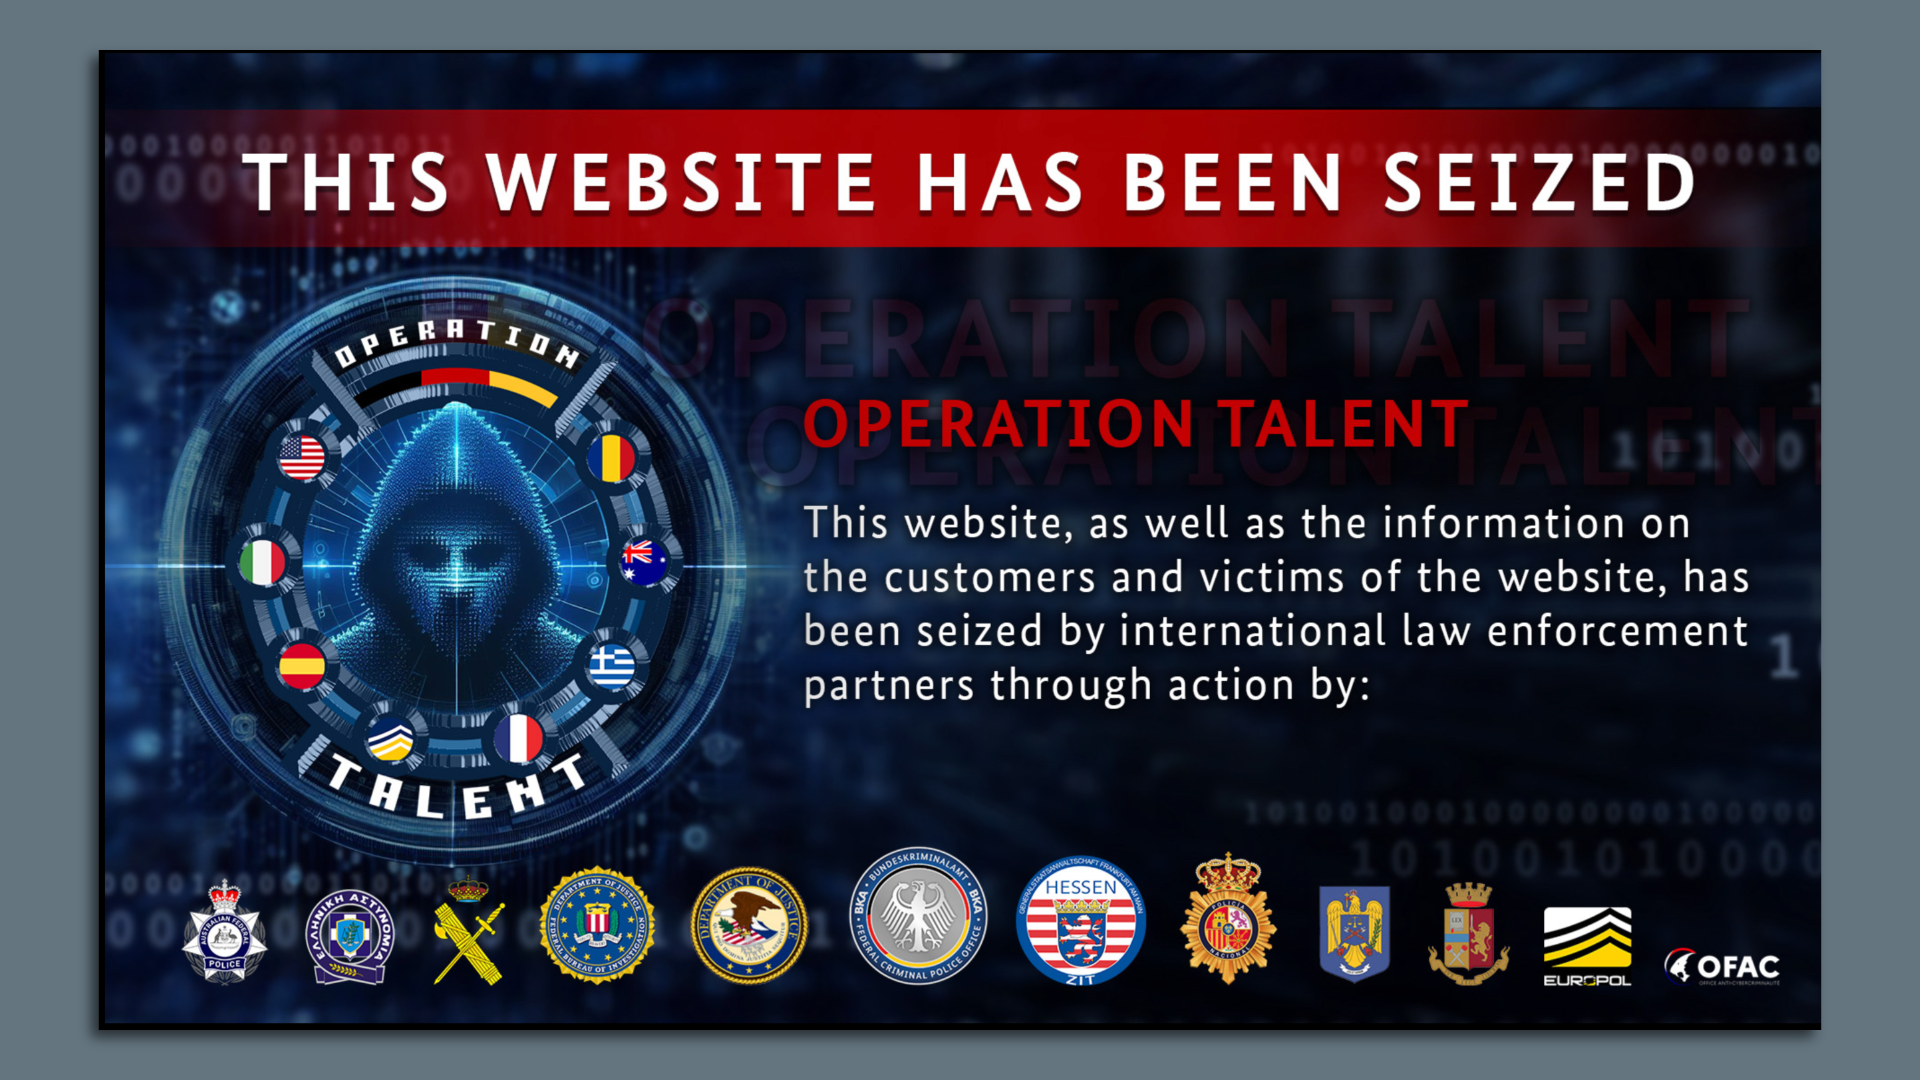
- "This website, as well as the information on the customers and victims of the website, has been seized by international law enforcement partners," the notice reads.
- Law enforcement from the United States, Italy, Spain, Europe, France, Greece, Australia and Romania each have a logo on the seizure notice.
- The FBI seized the domains for the Cracked and Nulled hacker forums, according to security researchers, and the forums' name servers are now listed as FBI addresses.
- One of Cracked's moderators said in a Telegram post Wednesday that the forum had "been seized" during an operation and that the forum was awaiting court documents from its data center.
- "A sad day indeed for our community," the moderator added.
Between the lines: Cracked and Nulled were both sprawling marketplaces where cybercriminals could sell software licenses, stolen login credentials and hacking tools.
- The DOJ estimates that Cracked had more than 4 million users and generated roughly $4 million in revenue. Tools and information sold on Cracked impacted at least 17 million U.S. victims.
- Nulled had more than 5 million users and generated around $1 million in revenue annually, the DOJ said in its release. A product advertised on Nulled claimed to have the names and Social Security numbers of 500,000 U.S. citizens.
Yes, but: Ethical hackers also used some of these forums to discuss their findings.
The big picture: The seizures are among a long list of international law enforcement operations targeting cybercriminals and their web operations in recent years, including the takedown of hacker site BreachForums and prolific ransomware gangs.
3. Catch up quick
@ D.C.
🏛️ Both Kash Patel, President Trump's pick to lead the FBI, and Tulsi Gabbard, his nominee to lead the intelligence community, were grilled in the Senate during their confirmation hearings yesterday. (Axios)
🔬 OpenAI is putting its models on a supercomputer at the Los Alamos National Laboratory and making the model available to researchers at other national labs. (Axios)
👨🏻⚖️ A new lawsuit claims that officials at the Office of Personnel Management bypassed a required privacy impact assessment before setting up an on-premise server to run its new government-wide email blast list. (FedScoop)
@ Industry
📈 CrowdStrike says it got a perfect score on an industry test for ransomware detection, protection and accuracy — sending its stock price soaring. (Barron's)
👀 OpenAI has accused DeepSeek of violating its terms of use by "inappropriately" using the ChatGPT maker's outputs to train its own models. (Axios)
👔 More than 8 in 10 CISOs now report directly to their company's CEO, a major jump from less than half who did so just two years ago, according to a new report. (Cybersecurity Dive)
@ Hackers and hacks
🤖 Chinese and Iranian hacker teams are using Google's Gemini and other AI models to bolster their cyberattacks, according to new Google research. (Wall Street Journal)
📲 Researchers have uncovered two vulnerabilities in Apple-designed chips powering Macs, iPhones and iPads that could leave them vulnerable to data leaks. (Ars Technica)
🩸 A New York-based blood center that serves more than 75 million people is battling a ransomware attack that's already forced officials to reschedule blood drives and come up with operational workarounds. (The Record)
4. 1 fun thing
🎶 It's finally Grammys weekend: Send me your predictions!
- 🔮 Fair warning: I deeply disagree with many of Rolling Stone's predictions of who will end up winning, but who knows — I don't have a working crystal ball (yet).
☀️ See y'all Tuesday!
Thanks to Megan Morrone for editing and Khalid Adad for copy editing this newsletter.
If you like Axios Codebook, spread the word.