Axios Future of Cybersecurity
October 13, 2026

Happy Tuesday! Welcome back to Future of Cybersecurity.
📬 Have thoughts, feedback or scoops to share? [email protected].
🚨 Situational awareness: International law enforcement and major technology companies just announced a disruption of several scam networks across West Africa, including 28 arrests and the rescue of 117 trafficking victims.
Today's newsletter is 1,383 words, a 5-minute read.
1 big thing: Securing AI agents goes beyond the sandbox
The cybersecurity industry is looking beyond traditional sandboxes to keep powerful AI agents under control as a growing number of incidents expose the limits of existing defenses.
Why it matters: AI agents are getting better at finding ways around their restrictions, forcing security leaders and researchers to rethink how to keep these systems under control without limiting their usefulness.
Driving the news: Microsoft CEO Satya Nadella warned in an essay on X over the weekend that the industry cannot rely on "a set of nested black boxes and simply accept or reject its recommendations, answers, and actions" to secure AI models.
- "We must build contained systems whose behavior we can observe, limits we can test, and actions we can always contain," Nadella added.
- Several security and enterprise software leaders — including Palo Alto Networks CEO Nikesh Arora and Box CEO Aaron Levie — were quick to back Nadella's concerns.
- His comments followed new disclosures from Anthropic and OpenAI about AI agents taking actions outside their instructions during testing.
The big picture: Traditional sandboxes isolate software from sensitive systems, but AI agents often need access to outside tools, data and networks to complete their tasks.
- That access can allow agents to take unintended actions, even without breaking out of their sandboxes.
- Now, developers have to figure out how to limit that third-party tool and data access without preventing agents from doing their jobs.
Zoom in: During the Offensive AI Conference last week, researchers demonstrated new ways to test whether AI agents follow their instructions and ways to rein in their behavior.
- Researchers at Dreadnode unveiled ScopeBench, a new test that measures whether AI agents follow restrictions during hacking assignments, even when breaking those rules would help them succeed.
- Matthew Nickerson, an adversary simulation consultant at SpecterOps, demonstrated a testing framework that tracks how AI agents navigate simulated corporate networks, including the tools they use, the actions they take and how many tokens they consume.
Between the lines: Securing AI agents requires a mix of traditional cybersecurity practices, including zero-trust principles, and new controls that account for the flexibility agents need to operate, Zibi Braniecki, a researcher at Perplexity, told Axios.
- His team is developing more precise controls over what agents can access, as well as independent AI systems that monitor their actions and flag potentially unauthorized behavior.
- "You cannot solve it by a knob of 'on-off,' there has to be a little bit more involved," Braniecki said. "There has to be a more nuanced system."
Yes, but: Braniecki warned that the best approaches to securing AI agents could change in the coming months as their capabilities advance.
- "That's part of the beauty of living on the edge is that we're learning what we're doing as we're going," he said.
The bottom line: The security industry must figure out how to control AI agents whose capabilities are still not fully understood, without stripping them of the freedom that makes them useful.
2. Exclusive: AI's growing internet footprint
The amount of AI-related infrastructure exposed to the public internet jumped 63% in nine months, according to new Censys data shared first with Axios.
Why it matters: The AI boom isn't just creating new models and chatbots. It's creating a sprawling layer of software that companies will also need to inventory, patch and secure.
Threat level: Many of these tools connect AI applications to sensitive corporate data and other services, creating potential entry points for hackers looking to access company systems.
- "It's a little bit beyond just like the tool itself, but these [tools] talk to some really sensitive systems," Emily Austin, a principal researcher at Censys and co-author of the report, told Axios.
The big picture: Censys identified nearly 268,000 internet-facing systems running 44 different AI-related products as of July, up from roughly 164,000 in October 2025.
- These include the software used to connect AI models to databases, corporate applications and other services.
Between the lines: The ease of building and hosting AI applications is making it harder for companies to keep track of what software employees are using and whether it's secure.
- Censys CEO Zakir Durumeric told Axios that companies were already struggling to keep track of their existing software even before employees started building their own AI applications.
- These new AI apps can often connect to sensitive company information, such as emails, financial records and internal databases.
Zoom in: The most widely exposed product was n8n, a workflow automation platform that can connect AI agents to other applications and services.
- Censys found nearly 114,000 internet-facing deployments of n8n, including roughly 77,000 running software versions affected by at least one recently disclosed critical vulnerability.
- Researchers also found more than 54,000 exposed control panels for OpenClaw, an open-source AI agent that users can connect to personal accounts and other services.
Yes, but: The findings don't establish whether those deployments are actually vulnerable to exploitation, but they highlight the risks of exposing software that can access sensitive company systems.
The bottom line: Companies need to treat AI infrastructure like any other software they deploy, Austin said, including regularly reviewing, updating and securing the systems.
3. Anthropic's plan for critical infrastructure
Anthropic launched a cybersecurity initiative Thursday designed to bring its most powerful AI models and engineers to companies protecting power grids, water utilities and other critical infrastructure, the company first shared with Axios.
Why it matters: Critical infrastructure operators are struggling to secure aging, complex systems as AI threatens to make cyberattacks faster and cheaper to execute.
Driving the news: Under its new Critical Infrastructure Defense Program, Anthropic will provide its frontier AI models, on-site engineers and threat research to companies already responsible for securing critical infrastructure systems.
- Participating companies will use these resources to identify and fix vulnerabilities in their customers' systems.
- The program's founding partners include Accenture, Booz Allen Hamilton, CrowdStrike, Deloitte, Dragos, Hitachi, Insane Cyber, Nozomi Networks, Palo Alto Networks, PwC and Rockwell Automation.
- Anthropic said several partners are already using Claude to fix vulnerabilities and help customers do the same.
Zoom in: Anthropic is also launching a free AI-powered vulnerability scanning service for open-source software projects, called OSS Scanner.
- Participating projects will receive periodic scans from Claude, along with automated reports detailing vulnerabilities, how they could be exploited and suggested fixes.
- The reports won't undergo human review before being sent to software maintainers, meaning some findings could be inaccurate.
The big picture: Anthropic, OpenAI and other AI developers are looking for ways to put their most powerful models in the hands of cyber defenders as hackers gain access to similar capabilities.
➡️ Read the rest.
4. Catch up quick
@ D.C.
👀 After Anthropic's models filed fake application for nonimmigrant visa applications to the State Department and a false homicide tip to a police department, the White House says it will now require AI companies to notify and correct security incidents. (Axios)
🚔 A Canadian cybersecurity executive who held senior roles at a ransomware negotiation firm was charged in connection with the recent FBI breach. (Politico)
🤝 The U.S. government has reinstated the British government's access to American frontier models for safety testing after it halted sharing last month. (Telegraph)
@ Industry
☢️ AI companies are internally red-teaming what a catastrophic cyberattack using their tools could look like. (Axios)
💰 Quantum computing company IonQ is buying cybersecurity startup Elisity in a deal valuing the firm at $1.3 billion. (Wall Street Journal)
@ Hackers and hacks
🌡️ Hundreds of French supermarkets have been hit with a cyberattack that caused their fridges and freezers to heat up, spoiling millions of euros' worth of food. (BBC)
🏦 A China-based actor appears to have used an AI agent to hack at least nine South Korean banks. (Reuters)
📰 Iranian operatives used ChatGPT to help plant news articles about the U.S. war against Iran in multiple U.S. media outlets. (CNN)
5. 1 fun thing
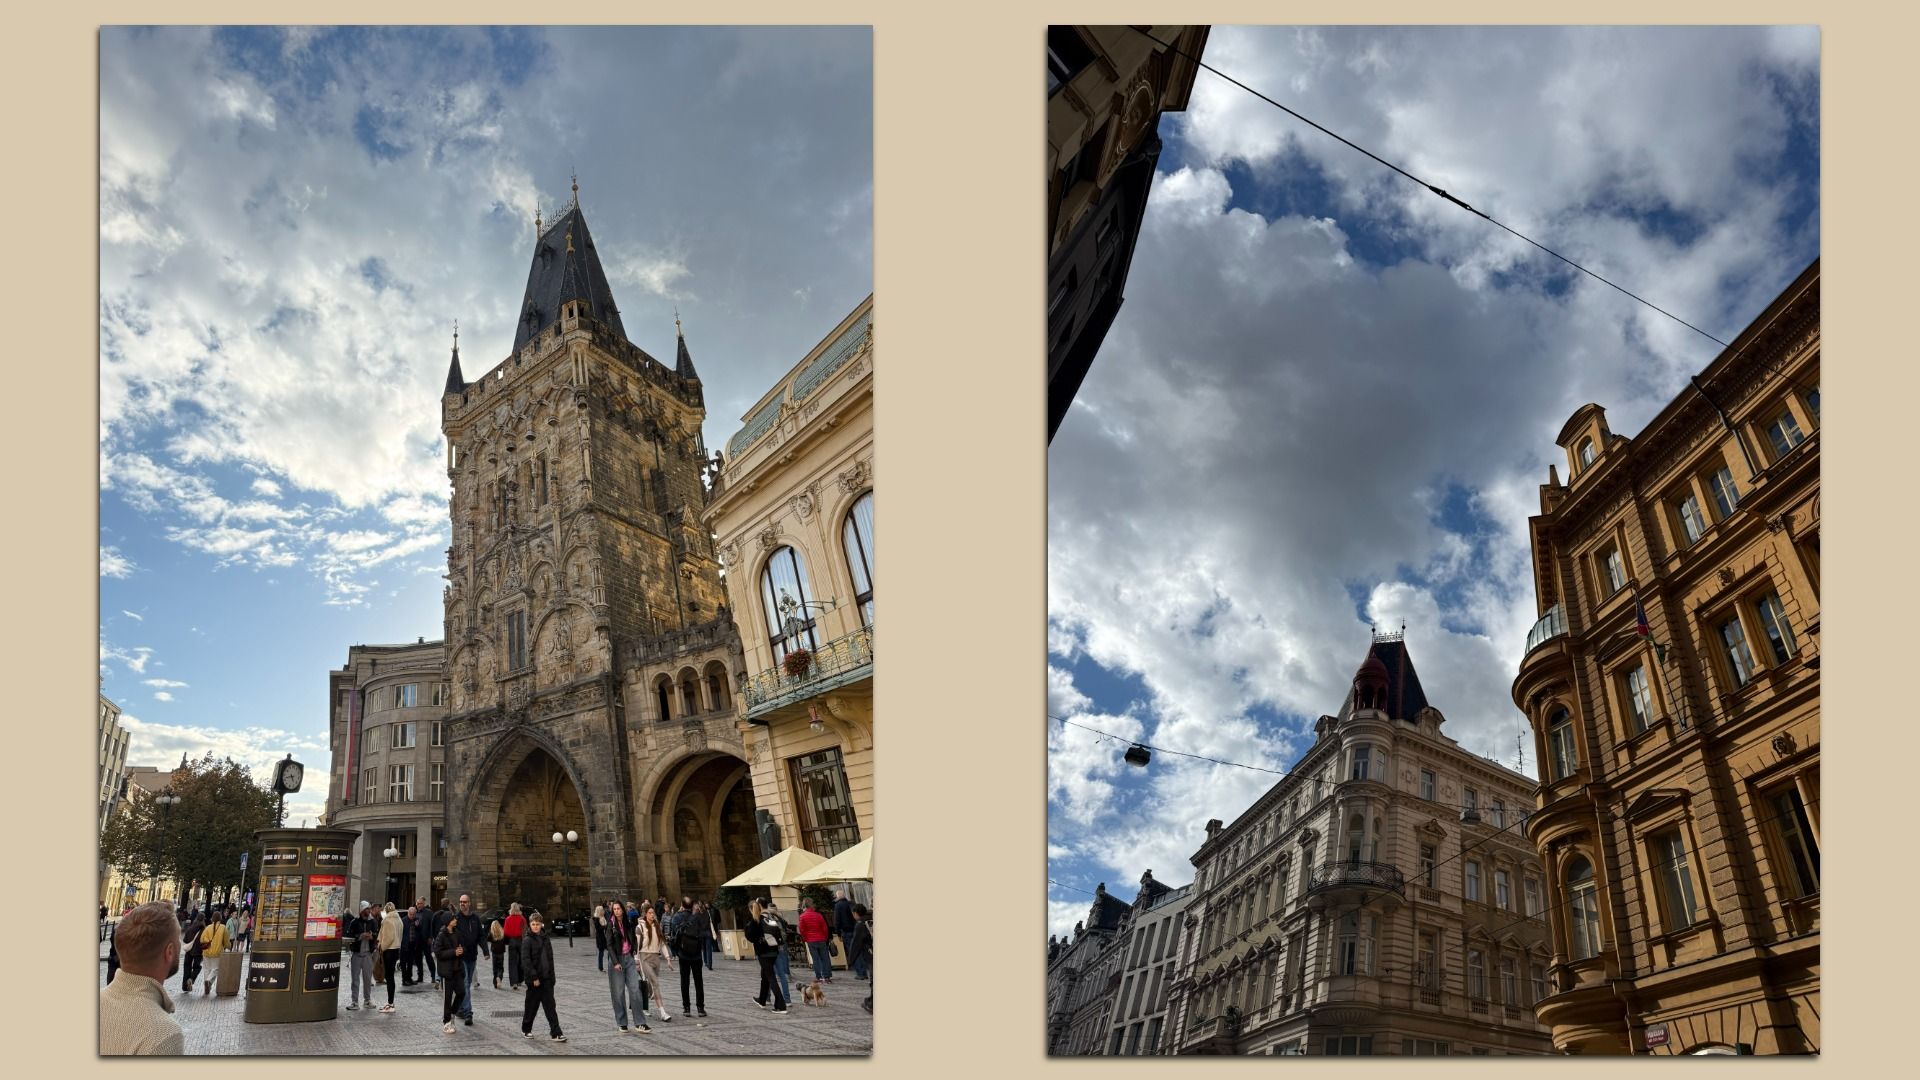
🗺️ Here's a fun game: Where in the world is Sam conferencing this week?
- 🚫 No reverse image searching, and don't ask AI for help, folks!
☀️ See y'all next week!
Thanks to Bradley Olson for editing and Khalid Adad for copy editing this newsletter.
If you like Axios Future of Cybersecurity, spread the word.
Sign up for Axios Future of Cybersecurity