Axios Future of Cybersecurity
October 20, 2026

Happy Tuesday! Welcome back to Future of Cybersecurity.
🇨🇿 Shoutout to the sole reader who successfully guessed I was in Prague last week! More from that reporting trip below.
📬 Have thoughts, feedback or scoops to share? [email protected].
Today's newsletter is 1,686 words, a 6.5-minute read.
1 big thing: A major open-source encryption tool is getting buried in AI requests
AI is helping secure one of the world's most widely used encryption libraries while simultaneously overwhelming the people responsible for maintaining it.
Why it matters: The challenges facing OpenSSL, one of the better-funded open-source software projects, offer a glimpse into how AI is straining the maintainers of software that businesses rely on every day.
Driving the news: OpenSSL received an average of 71 security reports and inquiries per month between May and July, up from just nine during the same period last year, OpenSSL Foundation executive director Matt Caswell said during the project's annual conference in Prague last week.
- That figure climbed to 108 inquiries in August, Caswell said.
- OpenSSL has received roughly 500 vulnerability reports over the past year. Just 63 resulted in disclosed vulnerabilities.
Threat level: The stakes are particularly high for OpenSSL, whose software helps secure communications across the internet.
- In 2014, the Heartbleed vulnerability in OpenSSL allowed attackers to extract sensitive information from vulnerable servers, potentially including passwords and encryption keys.
- The incident demonstrated how a flaw in a single widely used open-source library can put countless websites and services at risk.
Yes, but: Many of the reports are duplicates, minor software bugs or issues that don't warrant a security advisory, but each still requires human review, Caswell said.
- Most of the vulnerabilities uncovered by AI tools have been low-severity issues, rather than major security flaws.
The big picture: AI is making it easier to identify and fix vulnerabilities in widely used, volunteer-maintained open-source software, but the flood of discoveries is also exposing a shortage of experienced engineers who can determine which flaws pose real security threats.
- Maintainers for other popular encryption libraries, including Bouncy Castle and cryptlib, said at the conference that they're also dealing with an increased number of reports they need to review.
- Even OpenSSL, which has more financial resources than many other open-source projects, is struggling to keep pace with the influx of reports.
Between the lines: Even when AI tools propose a fix, humans are still needed to determine whether it works and approve changes to the code, creating a bottleneck.
- OpenSSL has roughly doubled its new contributors in the past year, but training engineers to become experienced reviewers takes much longer, Caswell said.
- The number of engineers authorized to approve code changes has grown from 18 in July 2024 to 30 as of this month, with most of that growth coming from engineering positions that OpenSSL has found funding to support.
- OpenSSL is reviewing and merging more code than ever before, but new submissions are arriving even faster, Caswell added.
What they're saying: "Those people are skilled individuals, and you can't create them overnight," Caswell told Axios about finding new engineers to review requests. "They don't grow on trees."
Zoom in: Caswell told Axios that AI tools are finding problems buried in obscure corners of OpenSSL's code that human researchers have historically overlooked.
- But it can take six to eight weeks to investigate a vulnerability, develop a patch and publish a security advisory, he added.
The intrigue: OpenSSL is deploying AI tools of its own to help review new code, investigate reported vulnerabilities and write software tests, Tomáš Mráz, chief technology officer at the OpenSSL Foundation, told Axios.
- Caswell said during a panel presentation that he now runs an AI code reviewer alongside his own manual reviews to catch problems he might otherwise miss.
- However, OpenSSL's maintainers still require human approval before accepting code changes.
What to watch: OpenSSL is urging more developers to help review code, rather than simply submit new contributions.
- Caswell said the project needs to train more experienced reviewers and secure additional funding to keep pace with the growing workload.
- "Critical open source is infrastructure, and we should be funding it as infrastructure," Caswell said during his presentation.
2. Scrambling to get frontier model access
In the race to fend off AI-enabled cyber threats, defenders are confronting a new problem: The AI models they're relying on to investigate attacks can suddenly refuse to help.
Why it matters: AI companies are developing specialized tools to help security teams respond to attacks faster, but restrictions on their most powerful models can leave them scrambling for alternatives in the middle of an investigation.
What's happening: OpenCode, an open-source AI coding agent, said it was compromised over the weekend, allowing attackers to obtain API keys belonging to some customers, including keys for OpenAI, Anthropic and Google services.
- OpenCode said the breach was "related to a large scale distillation attack that impacted 1.4% of OpenCode Console users."
- OpenCode co-creator Dax Raad said attackers had been targeting its systems continuously for 48 hours, forcing the company to keep its own AI agents running around the clock to respond.
- OpenAI, Google and Anthropic have said they worked with affected customers to revoke exposed API keys and address unauthorized usage charges.
Zoom in: Raad said on X that frontier AI models initially helped investigate the breach but then "started refusing."
- The models' safety restrictions reportedly began blocking requests as the investigation turned to potentially malicious code, even though OpenCode was trying to defend its own systems.
- OpenCode then gained access to OpenAI's Daybreak Blue program, which gives vetted cybersecurity defenders access to models with fewer restrictions.
- "We definitely need to be more proactive and we've made so many improvements over the last few days," Raad wrote on X yesterday.
The big picture: The incident underscored a dilemma facing cybersecurity teams trying to figure out when to use powerful proprietary AI models, which come with built-in restrictions, or open-weight alternatives that offer greater control over how they're deployed.
- When Hugging Face discovered suspicious activity on its systems that it later linked to OpenAI's own agents, its security team turned to a Chinese open-weight model to help investigate after encountering restrictions on frontier models.
Yes, but: AI companies maintain that they need to gate access to their most powerful models to ensure that malicious actors can't abuse their cyber capabilities.
Between the lines: Cybersecurity teams will have to figure out how to balance the need for faster AI-powered defenses with restrictions designed to keep those same capabilities out of attackers' hands, Chris Jones, chief technology officer at Nightwing, told Axios.
- "We're all going to have to figure out how that race gets modulated over time," Jones said. "That's a big piece here."
3. AI tools are aiding would-be spies
AI tools are now exacerbating a largely hidden problem that frontier AI companies have been contending with for years: the risk that employees will exploit their access to spy on their employers.
Why it matters: The same AI tools that companies are racing to release can also help people plan crimes and develop the technology to carry them out, creating another security headache for the companies building them.
Driving the news: Federal prosecutors last week charged Abdulrahman Alfozan, a Saudi national who has been an OpenAI engineer since July 2025, with attempting to intercept private conversations at OpenAI.
- Around Sept. 30, the company found a "surreptitious audio recording device" that was plugged into a USB port in the back of a television in an executive conference room.
- Prosecutors alleged in a court filing yesterday that Alfozan was "pursuing opportunities in Saudi Arabia before he was arrested" and that his family flew to Saudi Arabia after his arrest with a ticket "booked and paid for by the Saudi government."
Zoom in: Investigators allege Alfozan used AI tools to research company meeting rooms and develop recording equipment, according to an FBI affidavit.
- Alfozan used a "productivity agent" to ask basic information about OpenAI's offices, the documents say. Those queries included: "What meeting was this presented at and when was it record?," "List meeting rooms in [company] that are 6+", and "can you list today's meeting in this room."
- Investigators also said that an AI chatbot account tied to his spouse asked the model to build a "continuous audio recorder" and to add "browser access an controls," as well as encrypt the memory card where the recordings were saved.
- The complaint didn't say whether any sensitive conversations were successfully recorded.
The big picture: This is just the latest case where AI tools have helped people carry out alleged crimes.
➡️ Read the rest.
4. Catch up quick
@ D.C.
🗳️ Political appointees asked career CISA employees to procure a voting machine, probe it for vulnerabilities and compile a report for the White House. They refused. (ProPublica)
🛑 The Department of Homeland Security is banning DeepSeek's models from U.S. government IT systems. (CyberScoop)
📵 U.S. intelligence officials postponed a highly anticipated classified briefing for election officials about foreign threats because of technical difficulties with the video call. (CNN)
@ Industry
🤝 OpenAI is in talks to acquire cybersecurity firm Trail of Bits. (The Information)
📹 Flock CEO Garrett Langley defended the company's controversial surveillance technology, saying "it's worth it because there's millions and millions of people who have a better life today." (TechCrunch)
@ Hackers and hacks
🤖 A Chinese-speaking hacker broke into websites belonging to more than 100 companies and targeted more than 1,200 sites for roughly $5,000 worth of tokens. (Reuters)
🥸 Federal investigators believe that an executive for a U.S.-based consulting firm played a role in running the ShinyHunters hacking group's data extortion website. (KrebsOnSecurity)
🎯 Researchers at Citizen Lab uncovered a new spyware campaign where journalists were infected just by browsing past an ad on a website. (Wired)
5. 1 fun thing
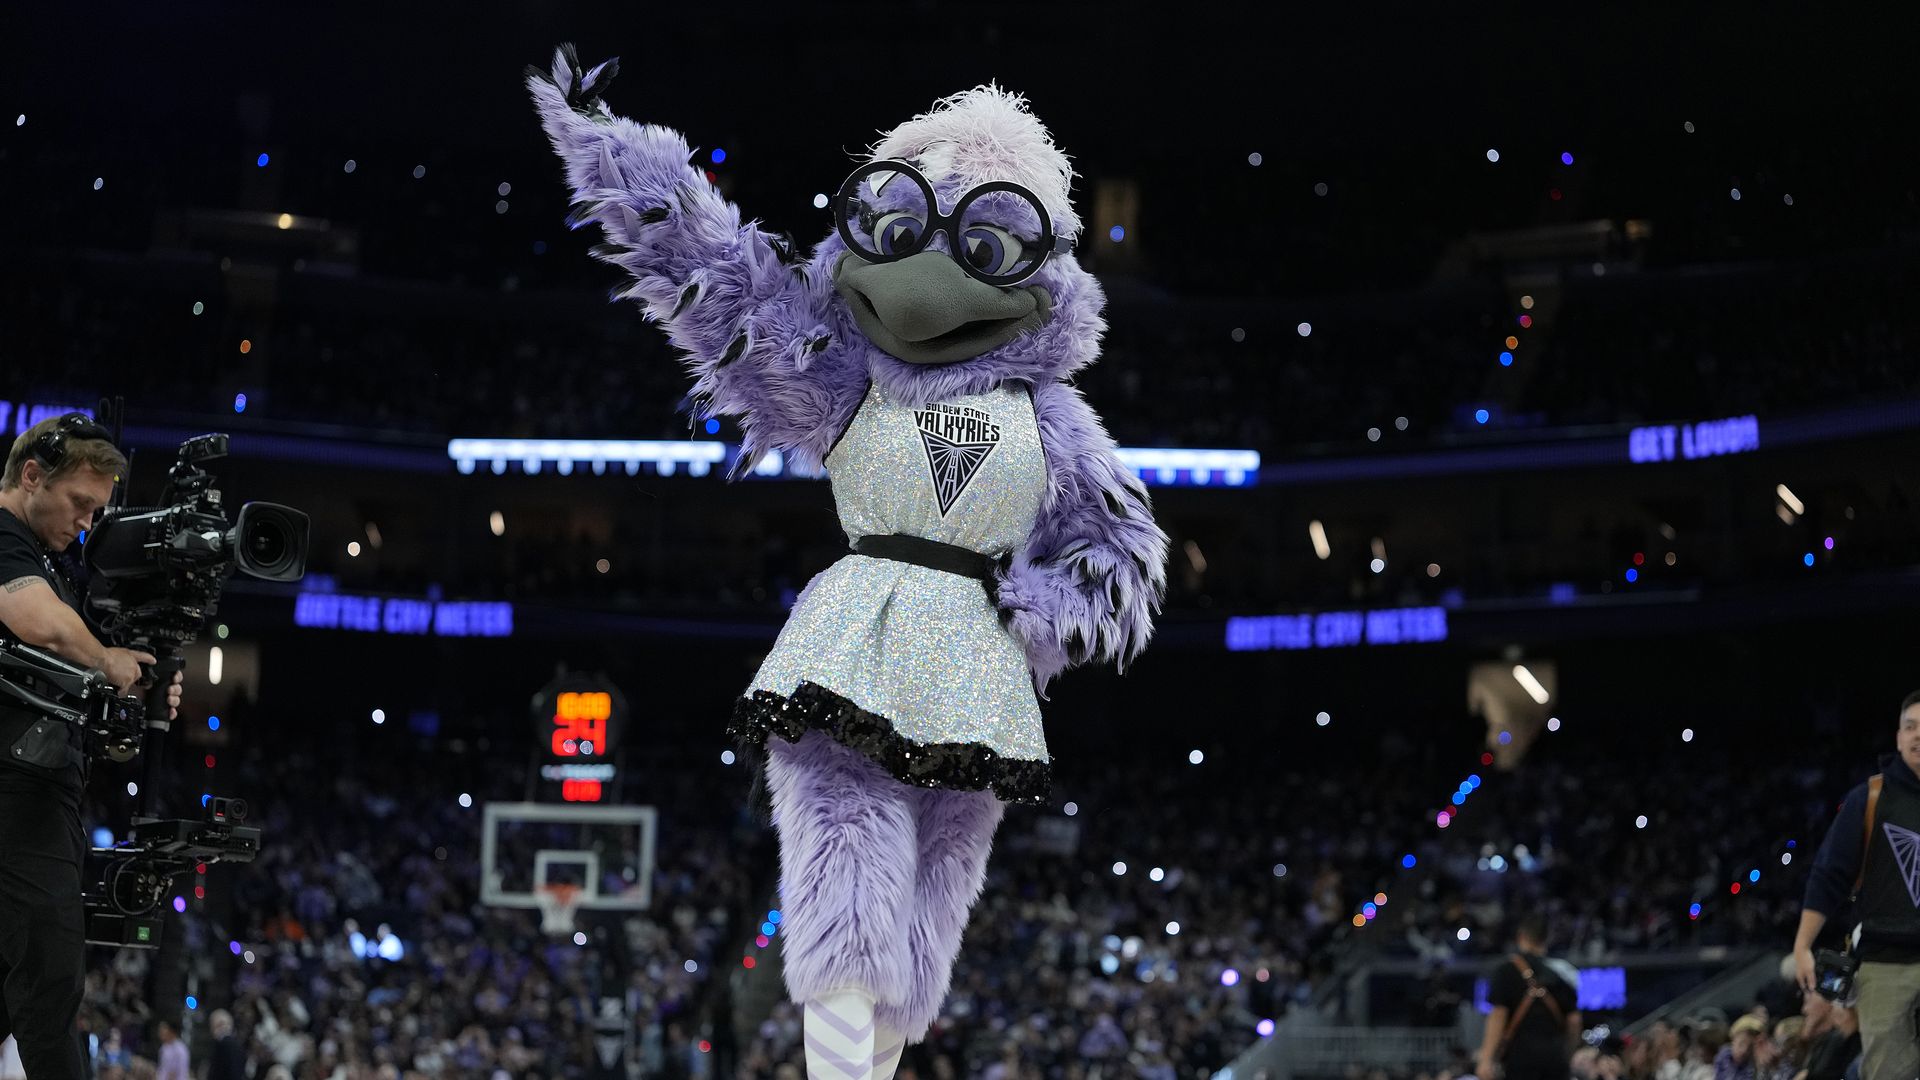
The Golden State Valkyries making it to the WNBA Finals is fun for a lot reasons — including that I now have an excuse to talk about their beloved mascot, who I'm obsessed with.
- For one: Look at her! She's fab.
- Secondly, just like me, she's near-sighted.
- Third, in the run-up to her debut last season, the Valkyries teased her arrival by live-streaming a giant purple egg for days. Incredible marketing!
☀️ See y'all next week!
Thanks to Bradley Olson for editing and Khalid Adad for copy editing this newsletter.
If you like Axios Future of Cybersecurity, spread the word.
Sign up for Axios Future of Cybersecurity