Axios Codebook
June 23, 2023

😎 TGIF, everyone. Welcome back to Codebook.
- My colleagues have important stories out today about abortion access for this weekend's anniversary of the Supreme Court's Dobbs decision. Give them a read.
- 📬 Have thoughts, feedback or scoops to share? [email protected].
Today's newsletter is 1,470 words, a 5.5-minute read.
1 big thing: A different kind of supply chain attack
Illustration: Aïda Amer/Axios
A pair of recent high-profile cyberattacks are putting a spotlight back on a hacking tactic that's growing in popularity.
The big picture: A number of supply chain attacks have already impacted organizations this year — and despite the name, the attacks have nothing to do with better-known trade supply chains.
- Instead, in the cybersecurity world, a supply chain attack refers to a cyberattack on companies' software vendors, or their software supply chain.
How it works: Supply chain attacks often start with hackers targeting a single entity — typically a software provider — in the hopes of accessing information from that organization's customers.
- To do this, malicious hackers will often add malware to the infiltrated product's software updates, build processes or source code to infect customers running the product on their own networks.
- One of the highest-profile recent supply chain attacks was the SolarWinds cyber espionage campaign, where Russian state-backed hackers snuck malware into a routine SolarWinds software update and infected nine federal agencies and at least 100 companies.
Driving the news: Recent headlines surrounding vulnerabilities in the MOVEit file-transfer program and Barracuda Networks' email security hardware have brought the spotlight back to software supply chain attacks.
- In the MOVEit case, a Russian ransomware gang has reportedly targeted federal agencies, state governments and other organizations by exploiting recently discovered security vulnerabilities.
- China-linked hackers are also believed to have targeted hundreds of organizations, including government agencies, through the Barracuda Networks security flaw.
Zoom out: Software supply chain attacks have been gaining traction in recent years.
- In 2021, a ransomware attack on IT management company Kaseya ended up affecting roughly 1,500 organizations.
- Later that year, a flaw in open-source program Log4j likely affected hundreds of millions of devices.
By the numbers: More than 10 million people and more than 1,700 organizations were affected by supply chain attacks in 2022, according to a report from the Identity Theft Resource Center.
Between the lines: Protecting against a software supply chain attack is tricky given that companies often have little visibility into their software vendors' cybersecurity programs.
- When a supply chain attack happens, each affected organization also ends up being reliant on the targeted software provider for information about the threat and patches to protect its systems.
The intrigue: Visibility also isn't as simple as knowing which vendors are on an organization's networks. Companies can also be at risk if there are vulnerabilities in their vendors' own software vendors.
- One example is the recent North Korea-linked 3CX supply chain attack, which researchers at Mandiant have said started as a cyberattack on another platform, X_Trader.
Yes, but: The Biden administration is pushing new initiatives to help bring greater visibility into organizations' networks.
2. Protecting your identity after MOVEit breaches
Ilustration: Rebecca Zisser/Axios
The number of people whose personal information has been exposed or stolen during a series of breaches related to the MOVEit file-transfer tool is continuing to grow — but security experts say there are still some practical steps individuals can take to protect their identities.
Why it matters: Once a malicious actor steals someone's identity, it's challenging and time-consuming for the individual to get it back and clean up the mess.
The big picture: Hackers are believed to have targeted a wide range of organizations — including federal agencies, state governments and corporate entities — using flaws in popular file-transfer tool MOVEit.
- Cl0p, the Russian ransomware gang reported to have exploited MOVEit vulnerabilities, has listed at least 95 organizations on its dark web site whom it says it has breached.
- State offices in California and Maryland, as well as a university system in Illinois, said this week they were investigating related breaches on their networks.
Between the lines: Data exposed in these breaches could end up being leaked on the dark web, where malicious actors can purchase it to steal people's identities, open fraudulent accounts or even access existing accounts.
- Many of the affected organizations have collected people's financial accounts and Social Security numbers — although it's unclear as of now whether hackers successfully stole that data from company networks.
Be smart: Zulfikar Ramzan, chief scientist at identity protection company Aura, told Axios there are several steps that consumers can take now to protect their identities in case hackers did steal their data.
- First, start monitoring your credit report for signs of new accounts created in your name.
- Next, change your passwords — especially the ones tied to leaked email addresses — and consider using a password manager that can store and create unique, difficult-to-guess passwords for each account, Ramzan said.
- Then, sign up for a data broker opt-out program that will wipe any personal data that marketers have collected about you online. The data that brokers collect can make it easier for scammers to impersonate you, Ramzan said.
- Lastly, use dark-web-scanning tools to see what passwords have been leaked already to figure out what other accounts might need an update.
Yes, but: There's no guarantee that every targeted organization will know it's been impacted or will alert affected consumers if their data was stolen.
3. Google invests $20M in cybersecurity clinics
Illustration: Sarah Grillo/Axios
Google is investing $20 million to stand up and expand 20 cybersecurity clinics at universities across the U.S., the company announced Thursday.
Why it matters: Cybersecurity clinics — akin to clinics at law schools where students provide discounted legal aid to specific groups — help local, under-resourced organizations get the cyber assistance they need, while also training a new crop of cyber workers to ease the ongoing worker shortage.
What they're saying: "At Google, we feel a deep sense of responsibility to help people find good-paying jobs in technology," Google CEO Sundar Pichai said during an event in D.C. on Thursday.
- "We also want to ensure that as a nation, we have a strong cybersecurity workforce to help us stay ahead of new, evolving threats," he added.
Details: Google is working with the Consortium of Cybersecurity Clinics to invest $20 million to both create new cybersecurity clinics and expand existing clinics at colleges and universities.
- Part of the funding will also go toward scholarships for students at these schools who want to get Google's cybersecurity certificate.
- A Google employee will serve as a mentor for the clinics at most locations, Pichai said.
- Applications for the funding will open in October, according to Google, and funds will be awarded in March. Selected organizations will receive up to $1 million.
How it works: Cybersecurity clinics bring undergraduate students to the cyber front lines.
- Typically, students enroll in a class tied to the clinic where they both learn basic cybersecurity skills and partner with local organizations and businesses to create a new cybersecurity strategy for them.
The big picture: Cybersecurity clinics have already started cropping up at a couple universities in recent years.
- The University of California, Berkeley, led the way in 2018, and others have followed in recent years at Indiana University, MIT and elsewhere.
Between the lines: Google promised in 2021 to invest $10 billion over the following five years to strengthen cybersecurity across the industry.
- The company also promised to train 100,000 Americans in data privacy and security through its career certificate program. Pichai said Thursday the company has already trained and certified twice that many in the U.S.
Yes, but: Solving the cyber workforce shortage is no small task.
- The U.S. has enough cybersecurity workers to fill only 69% of the available cyber roles, according to data from CyberSeek.
4. Catch up quick
@ D.C.
🚔 The U.S. Justice Department has created a new cyber-focused section inside its national security division that will help the department speed up operations and arrests against nation-state cyber threats. (CNBC)
🏛️ Lawmakers are weighing changing a controversial surveillance program so that conducting searches in a key database will require the FBI to obtain a warrant. (Wall Street Journal)
🙃 A year after the Dobbs decision, lawmakers have done little to protect people's sensitive health information from law enforcement inquiries. (CyberScoop)
@ Industry
📲 V Pappas, TikTok's most visible U.S. executive, is stepping down from the chief operating officer position. (Axios)
👨🏻⚖️ A proposed class action has been filed against Progress Software Corp. regarding the recent MOVEit-related breaches. (Bloomberg Law)
🎤 More than 100 musicians are boycotting venues that use facial recognition technology at live events. (Engadget)
@ Hackers and hacks
🧩 Apple patched a pair of critical security flaws that "may have been actively exploited." (Ars Technica)
💽 Dole said personal data belonging to 3,885 U.S. employees was breached during a February ransomware attack. (Cybersecurity Dive)
📝 Local governments are struggling to figure out how to publicly discuss details about ongoing ransomware attacks without interfering with ongoing criminal investigations. (CSO)
5. 1 fun thing
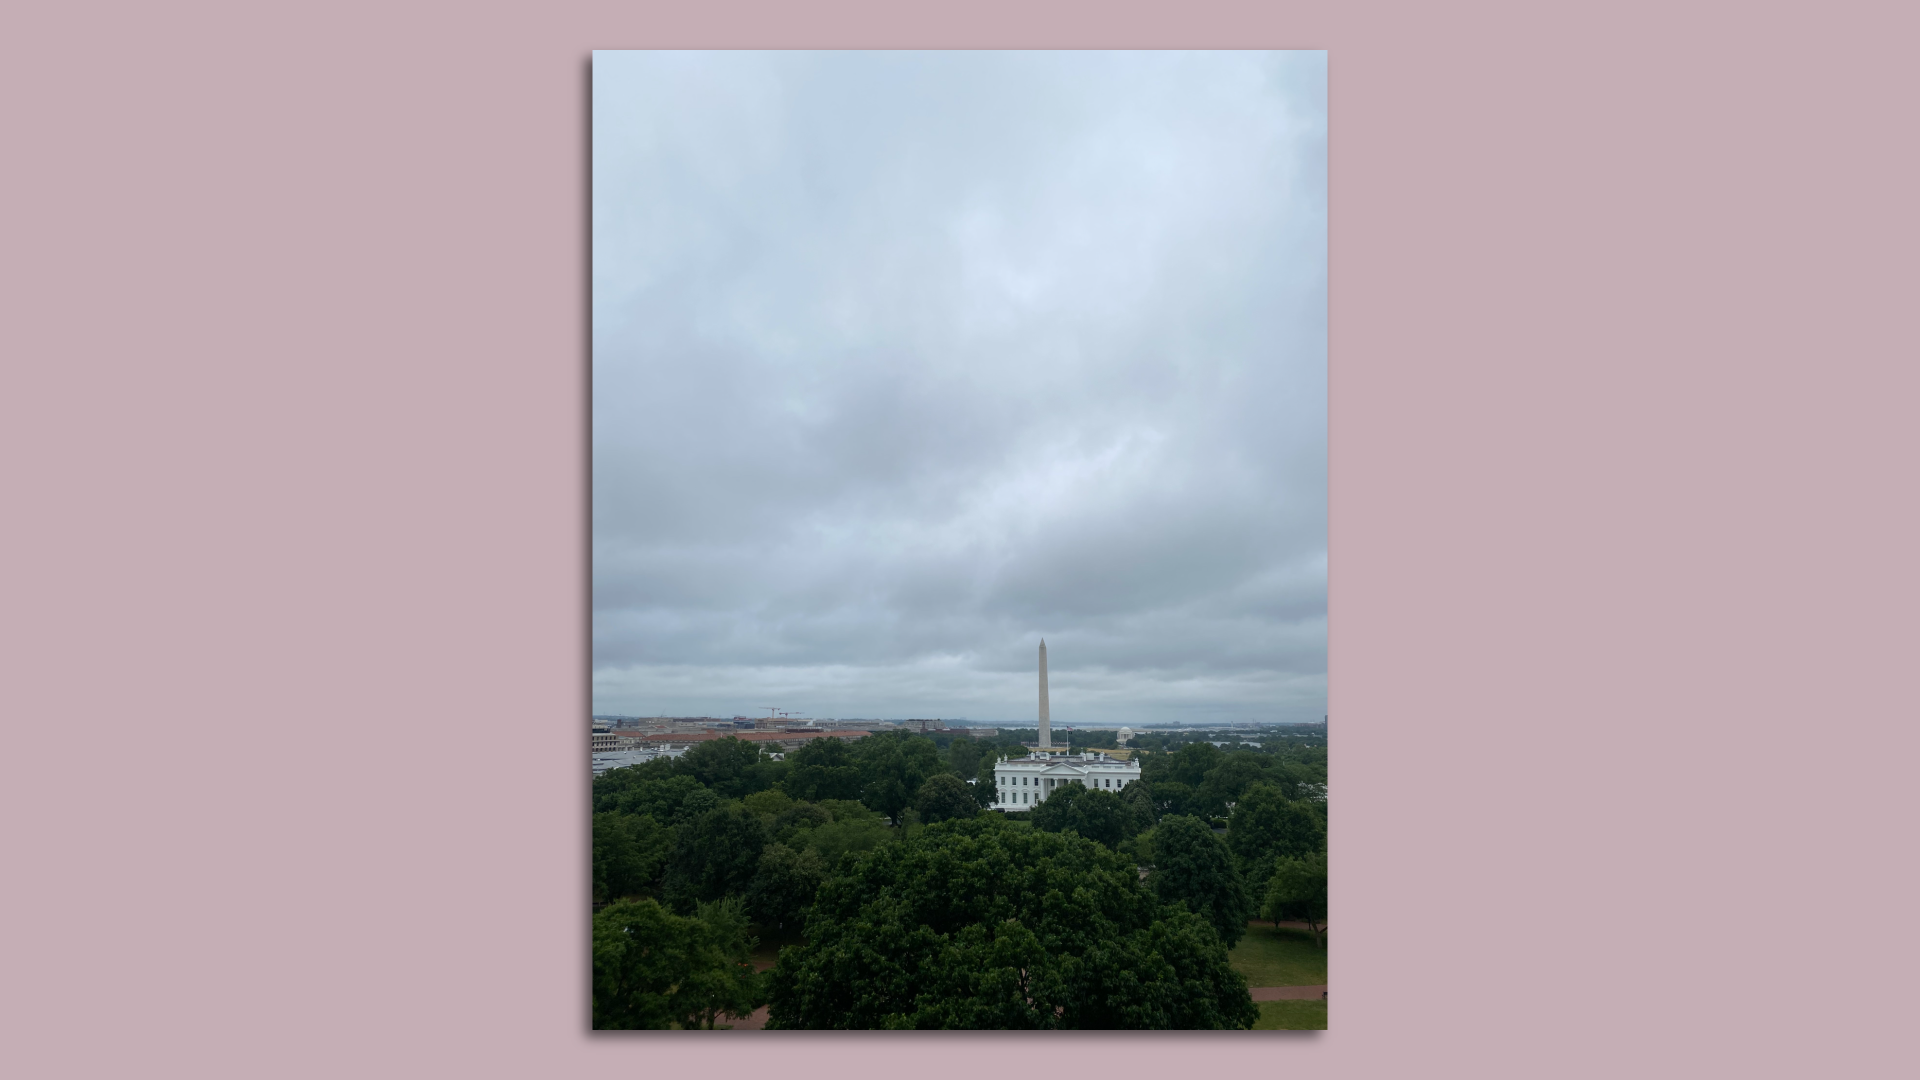
View of the White House from the Hay-Adams hotel in D.C. Photo: Sam Sabin/Axios
The best part about attending live events in downtown D.C. is the views from event venues.
- Today's is from the balcony at the Hay-Adams — thanks to the Financial Times for hosting its cyber summit this week at a place with such a lovely view.
☀️ See y'all on Tuesday!
Thanks to Scott Rosenberg for editing and Khalid Adad for copy editing this newsletter.
If you like Axios Codebook, spread the word.