Axios Codebook
February 10, 2023

😎 TGIF, everyone. Welcome back to Codebook.
- I somehow got Beyoncé tickets during the chaos of our company work retreat earlier this week! If you're still eagerly awaiting your city's presale, read on to see how the process went.
- 📬 Have thoughts, feedback or scoops to share? [email protected].
Today's newsletter is 1,319 words, a 5-minute read.
1 big thing: Reporting bugs just got easier for hackers
Illustration: Shoshana Gordon/Axios
A group of Austin-based, ethical hackers have become the first hacking collective to join a formal, global reporting program for disclosing software flaws.
Why it matters: Not all hackers are malicious or actively looking to exploit the security vulnerabilities they uncover. But the process of reporting the bugs they find is often arduous and, in some cases, full of legal headaches.
- Because of that, not all hackers end up reporting the bugs they find. Many vendors might not respond, don't understand the problem or might even issue cease-and-desist letters.
Driving the news: Austin Hackers Anonymous (AHA!) joined the internationally recognized CVE program earlier this week.
- In doing so, the group became what's known as a CVE Numbering Authority (CNA), which gives them more muscle when approaching companies about the security flaws they find while tinkering around in their free time.
Zoom out: Most major cybersecurity vendors participate in the program, allowing everyone to use the same standardized process of labeling and releasing details about new security vulnerabilities.
- For example, when vendors or researchers refer to the widespread Log4j vulnerability, they use the number CVE-2021-44228 to make sure they're all responding to the exact same issue.
The big picture: AHA! is now the first unorganized hacker collective in the country to be a CNA — giving anyone who presents at one of the group's meetings a clear way to register, report and publish the vulnerabilities they uncover.
- "I’ve been spending a lot of my career lately on getting vendors on board with this whole vulnerability-disclosure religion," Tod Beardsley, one of the founders of AHA!, told Axios.
- "Then it occurred to me that I sure need to do a lot more work on educating hackers on how this works, too," he added.
How it works: On the last Thursday of each month, AHA! members present their latest security discoveries in short, 10-minute presentations in the back room of a local bar.
- After, if presenters want to report their findings to the vendor, Beardsley kickstarts the process for the vulnerability at the meeting and discusses with the hacker if they want their name attached or if they want to remain anonymous.
- Beardsley expects he'll be the one to discuss the flaw with the vendor given his experience running another CNA program for his day job with security firm Rapid7.
The intrigue: Before the group became a CNA, AHA! members weren't always motivated to navigate the process on their own, Beardsley told Axios.
- Most members are just finding these vulnerabilities while messing with products for fun in their free time.
- And many companies are either quick to dismiss the claims from individual hackers disclosing a problem or are intimidated when a hacker approaches out of the blue about something they found.
- "The first response is often, 'Are you trying to sue us? Are you trying to extort us? Are you trying to sell us something?'" Beardsley said.
- Reporting through a recognized CNA program, rather than a solo hacker, gives these reports more legitimacy.
Between the lines: Austin is a burgeoning tech hub with plenty of talented hackers who discover major flaws all the time.
- Beardsley is hopeful the new AHA! program will lead to more bugs being reported and patched.
What's next: The first meeting where AHA! members can start registering their vulnerabilities is Feb. 23, and Beardsley said it usually takes a couple of months to work with companies to respond to the vulnerabilities before publication.
2. New sanctions for Trickbot
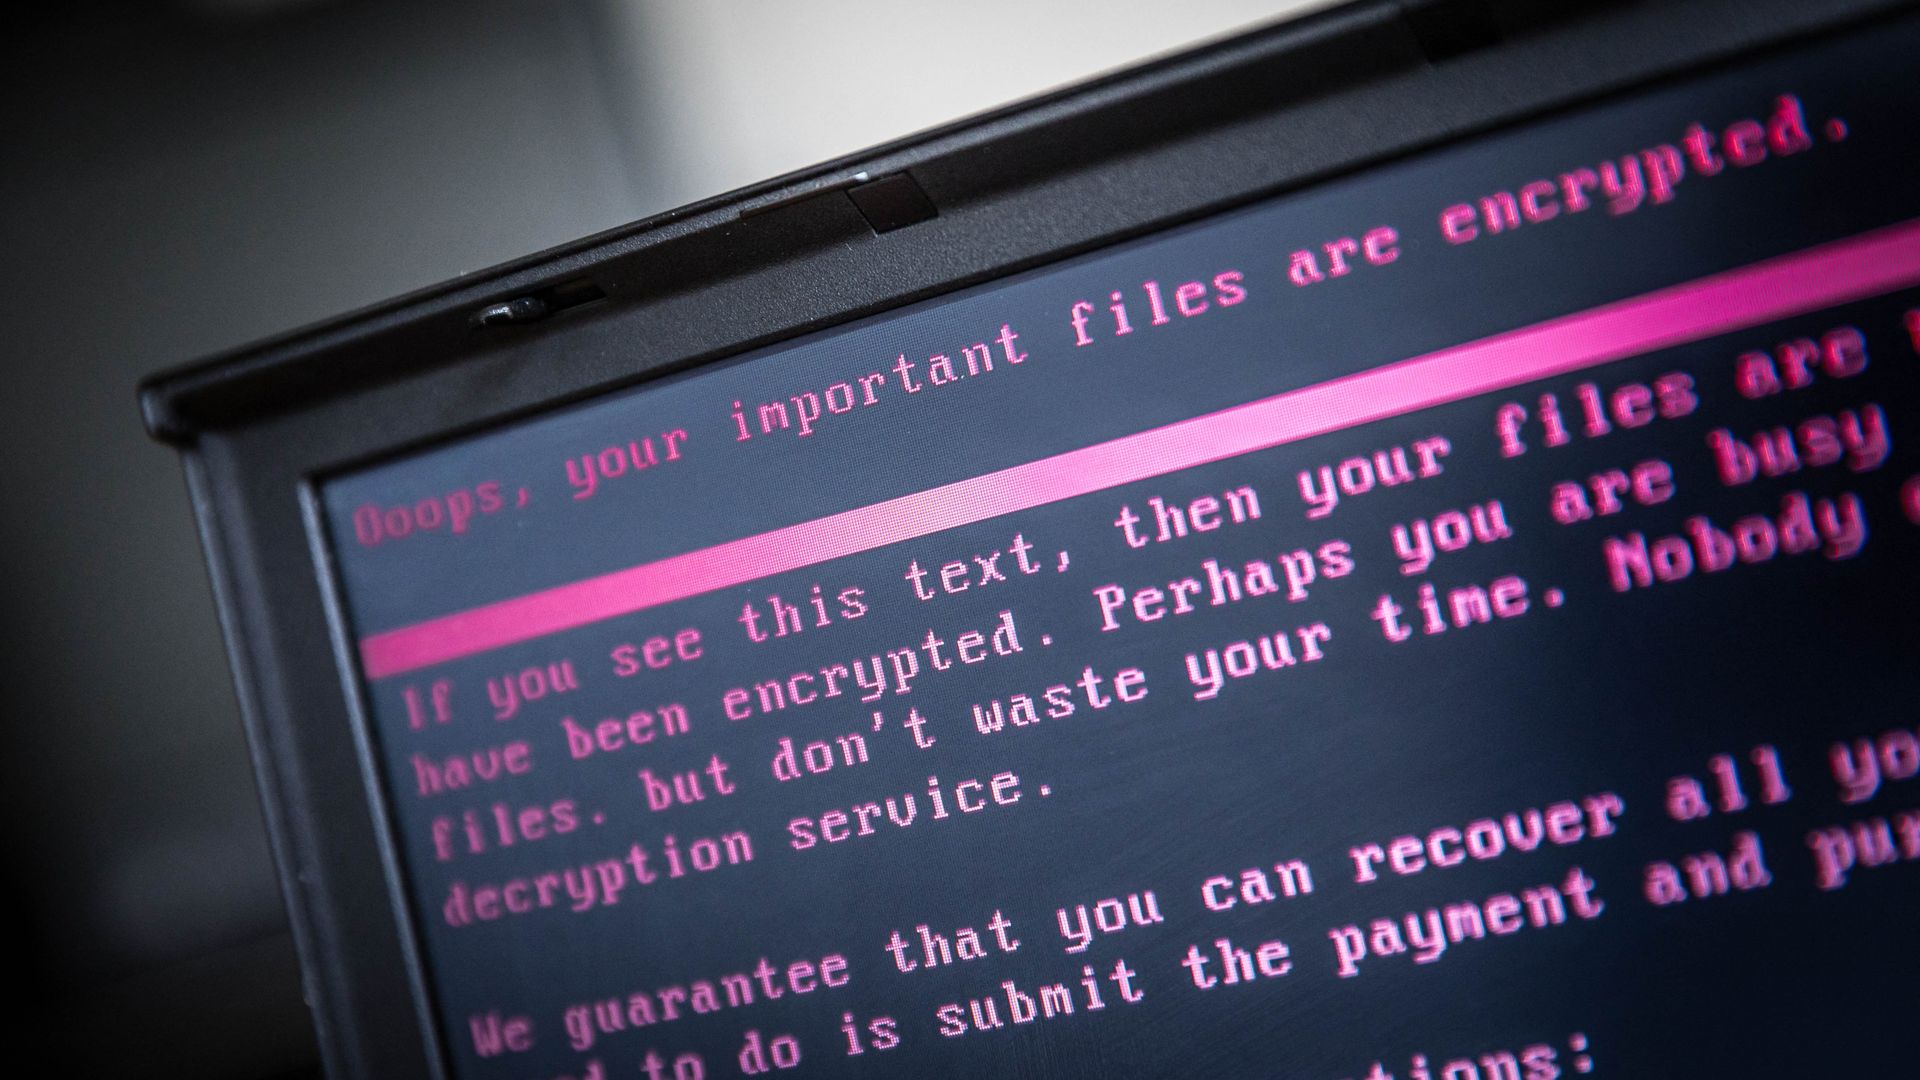
Photo: Rob Engelaar/ANP/AFP via Getty Images
The Treasury Department, in coordination with U.K. officials, sanctioned seven individual members of the notorious Russian hacking gang Trickbot, which has targeted U.S. hospitals and businesses in the last three years.
Why it matters: Sanctions are one of the few recourses Western officials have to hinder Russian hackers.
- Sanctioned entities and people can't hold U.S. assets, and U.S. organizations can face legal consequences if they pay ransoms to sanctioned cybercrime groups.
The big picture: Trickbot has become one of the most notorious Russian ransomware gangs in recent years.
- The Treasury Department says the gang was behind a wave of cyberattacks on U.S. hospitals during the height of the COVID-19 pandemic.
- One such attack involved deploying ransomware on three Minnesota health care facilities in October 2020, disrupting the facilities' communications networks and forcing them to divert care to other facilities.
- Trickbot members have also gloated in internal messages about how easy it is to attack and get a ransom payment from health care organizations, as Wired reported.
Catch up quick: The U.S. Cyber Command attempted in 2020 to take down Trickbot's botnet, or a series of malware-infected devices that the hackers control.
- But the operation only temporarily hindered the group. More than 140,000 victims were hit with a new Trickbot ransomware strain in the year after Cyber Command's operation, according to Check Point Research.
3. The latest in the VMware ransomware campaign
Illustration: Aïda Amer/Axios
Nearly 19,000 VMware ESXi servers remain vulnerable to an ongoing, global ransomware attack targeting a two-year-old security vulnerability, according to a Rapid7 blog post published Thursday.
Catch up quick: In the last week, government agencies and researchers have been scrambling to get vulnerable organizations the tools they need to either patch their servers or decrypt their systems.
- Here's what we learned this week:
The Cybersecurity and Infrastructure Security Agency made an unusual move and published a recovery script Tuesday evening to help victims of the ESXiArgs ransomware unlock affected files.
- The agency warned that any organization should "carefully review the script to determine if it is appropriate for their environment before deploying it."
Hackers have started deploying a new ransomware strain against vulnerable VMware servers that encrypts even more data and makes recovery more difficult, BleepingComputer reported late Wednesday.
- Nearly 900 IP addresses had displayed a ransom note from the new ransomware strain as of Thursday, according to data from crowdsourced platform Ransomwhere.
- Some victims have now said that they had disabled the part of their VMware server affected by the two-year-old vulnerability — yet they were still breached and encrypted, per BleepingComputer.
A Florida state court system and several universities in the U.S. and Europe appear to be among the list of possible victims, Reuters reported.
- The Florida Supreme Court confirmed the ransomware had targeted a system outside of the court's main network.
Yes, but: It's still unclear who is behind the ongoing campaign and how much damage they're actually causing.
4. Catch up quick
@ D.C.
🧳 Chris Inglis, the first-ever national cyber director, will officially step down from his role on Wednesday. (CNN)
🤳 A year after the ID.me controversy, the company's ID verification tool remains the only option taxpayers have to access the IRS' online service. (CyberScoop)
🇰🇵 The National Security Agency, in coordination with South Korean officials, released details about the tactics and motivations behind North Korean state-sponsored hackers' attacks on critical infrastructure. (NSA)
@ Industry
📲 1Password will start supporting biometric-based passkeys this spring. (The Verge)
🏨 InterContinental Hotels is looking to dismiss a lawsuit from franchised hotel owners affected by a cyberattack last year. (Wall Street Journal)
👔 GitHub is laying off 10% of its staff and moving to a remote-first workplace model. (TechCrunch)
@ Hackers and hacks
💥 Reddit says it suffered a cyberattack last weekend where hackers were able to steal internal documents and source code. (BleepingComputer)
🇺🇦 Ukrainian cyber officials have uncovered an ongoing phishing attack impersonating various Ukrainian and Polish government agencies. (CERT-UA)
🚔 LockBit's high-profile ransomware attacks could make it a prime target for law enforcement action. (CyberScoop)
5. 1 fun thing
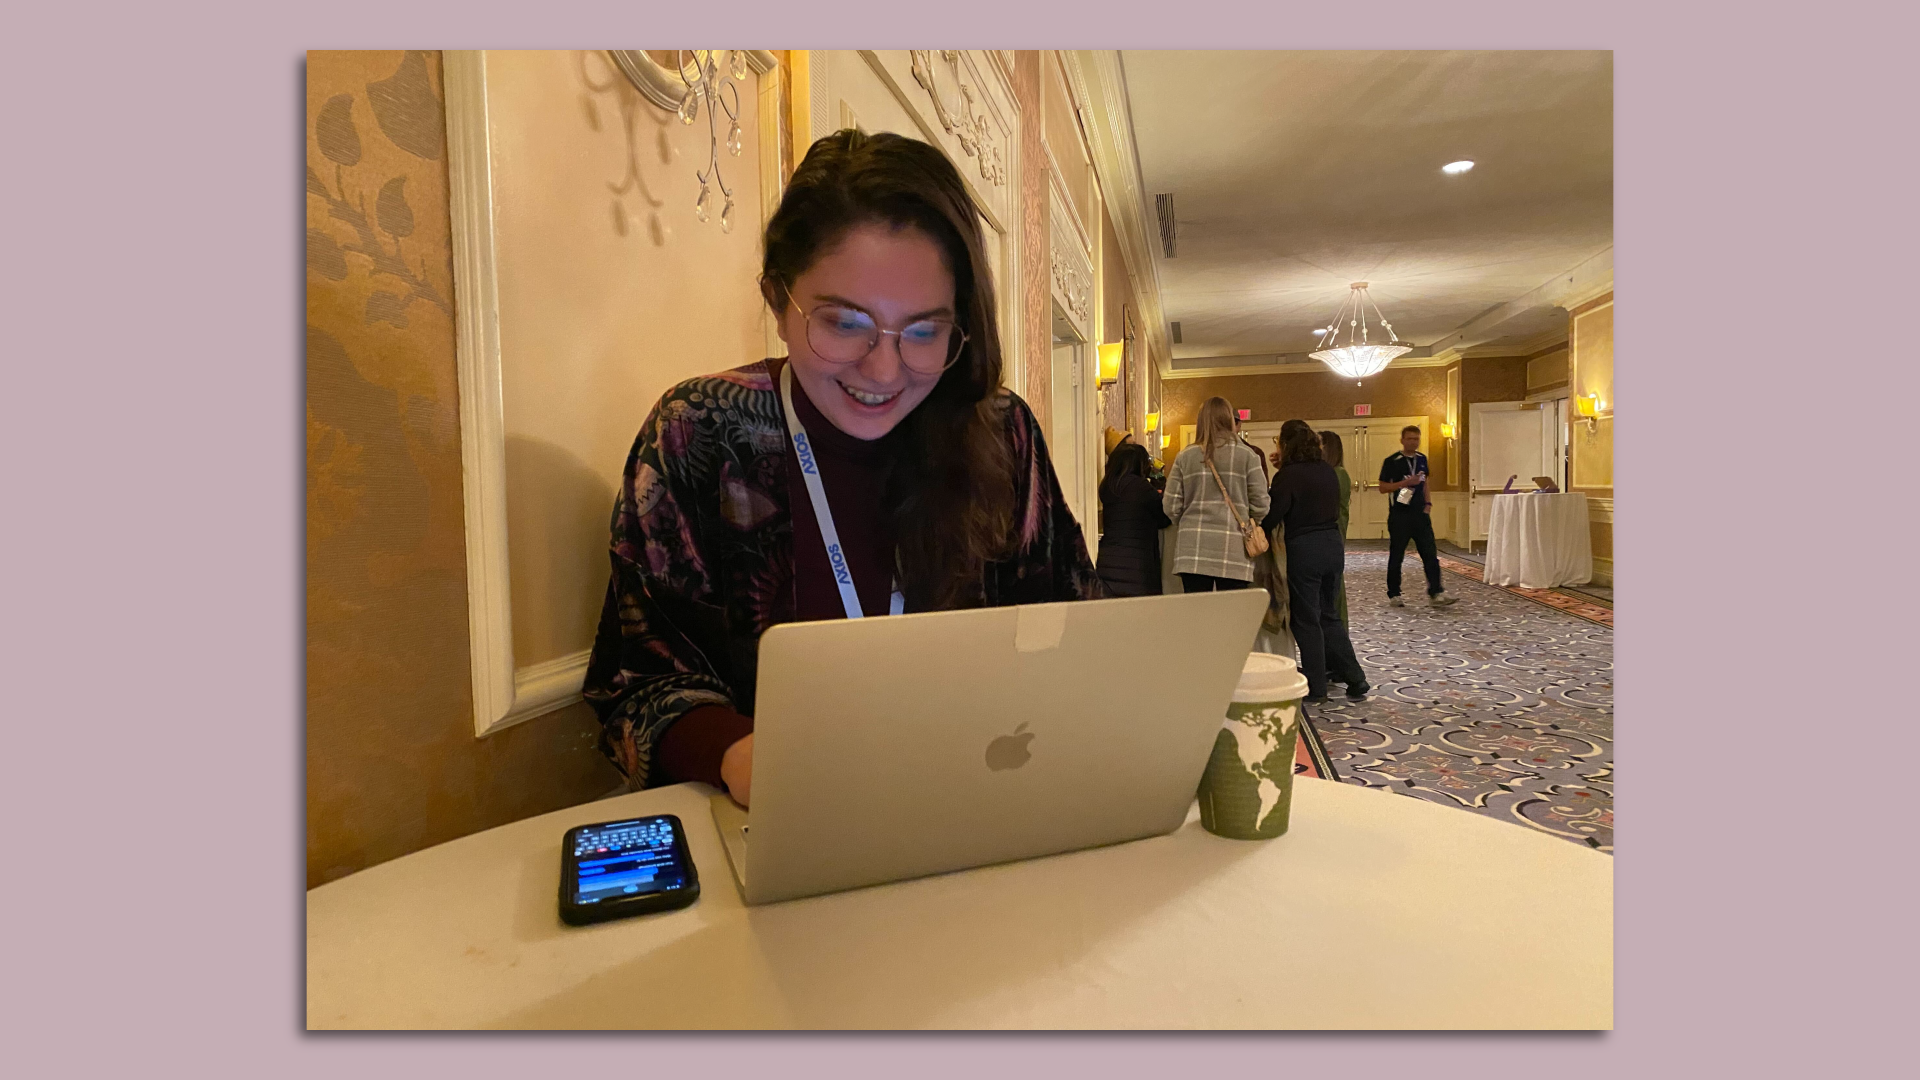
The moment the Beyoncé tickets were secured. Photo: Mackenzie Weinger/Axios
Corporate retreats are especially great at fostering team-building and letting employees pause and rest. And I used that renewed energy to immediately face my greatest feat this week: securing Beyoncé tickets.
- The process was surprisingly smooth (especially compared to last year's Taylor Swift debacle): Within 15 minutes, I had gone through the queue, picked out my seats, frantically texted the friend going with me and purchased two tickets.
- Huge thanks to Mackenzie Weinger, Axios Pro's new senior policy editor, for capturing my deliberations. I'm still in shock this happened.
☀️ See y'all on Tuesday!
Thanks to Peter Allen Clark for editing and Khalid Adad for copy editing this newsletter.
If you like Axios Codebook, spread the word.